Find exposed data everywhere it lives. Fix it in a click.
Secrets, PHI, PCI, and PII spread across dozens of SaaS apps in seconds, shared with personal accounts, ex-employees, and the open internet. Nightfall discovers it with 95% precision, scores the risk, and remediates thousands of exposures at once.
Sensitive data is hiding everywhere. Permission chaos reigns.
Built-in DLP from CASB, SASE, or app-native tools relies on basic pattern matching, overwhelms teams with false positives, and can’t centralize monitoring across the apps that matter. Meanwhile, the average organization has thousands of inappropriately shared documents nobody can see.
Two problems, one root cause: you can’t fix exposure you can’t find, and you can’t find it with regex.
Regex and pattern matching miss the contextual nuances that separate a real exposure from noise.
IT teams spend days manually correcting sharing settings, one file at a time.
Accidental public links, personal-account shares, and access that outlived the employee or vendor.
Incomplete offboarding leaves critical documents open to people who no longer work for you.
Discover. Score. Remediate at scale.
API-based integrations with over a dozen SaaS apps, AI detectors with 95% precision, and bulk remediation that fixes thousands of exposures in a few clicks.

API-based SaaS integrations
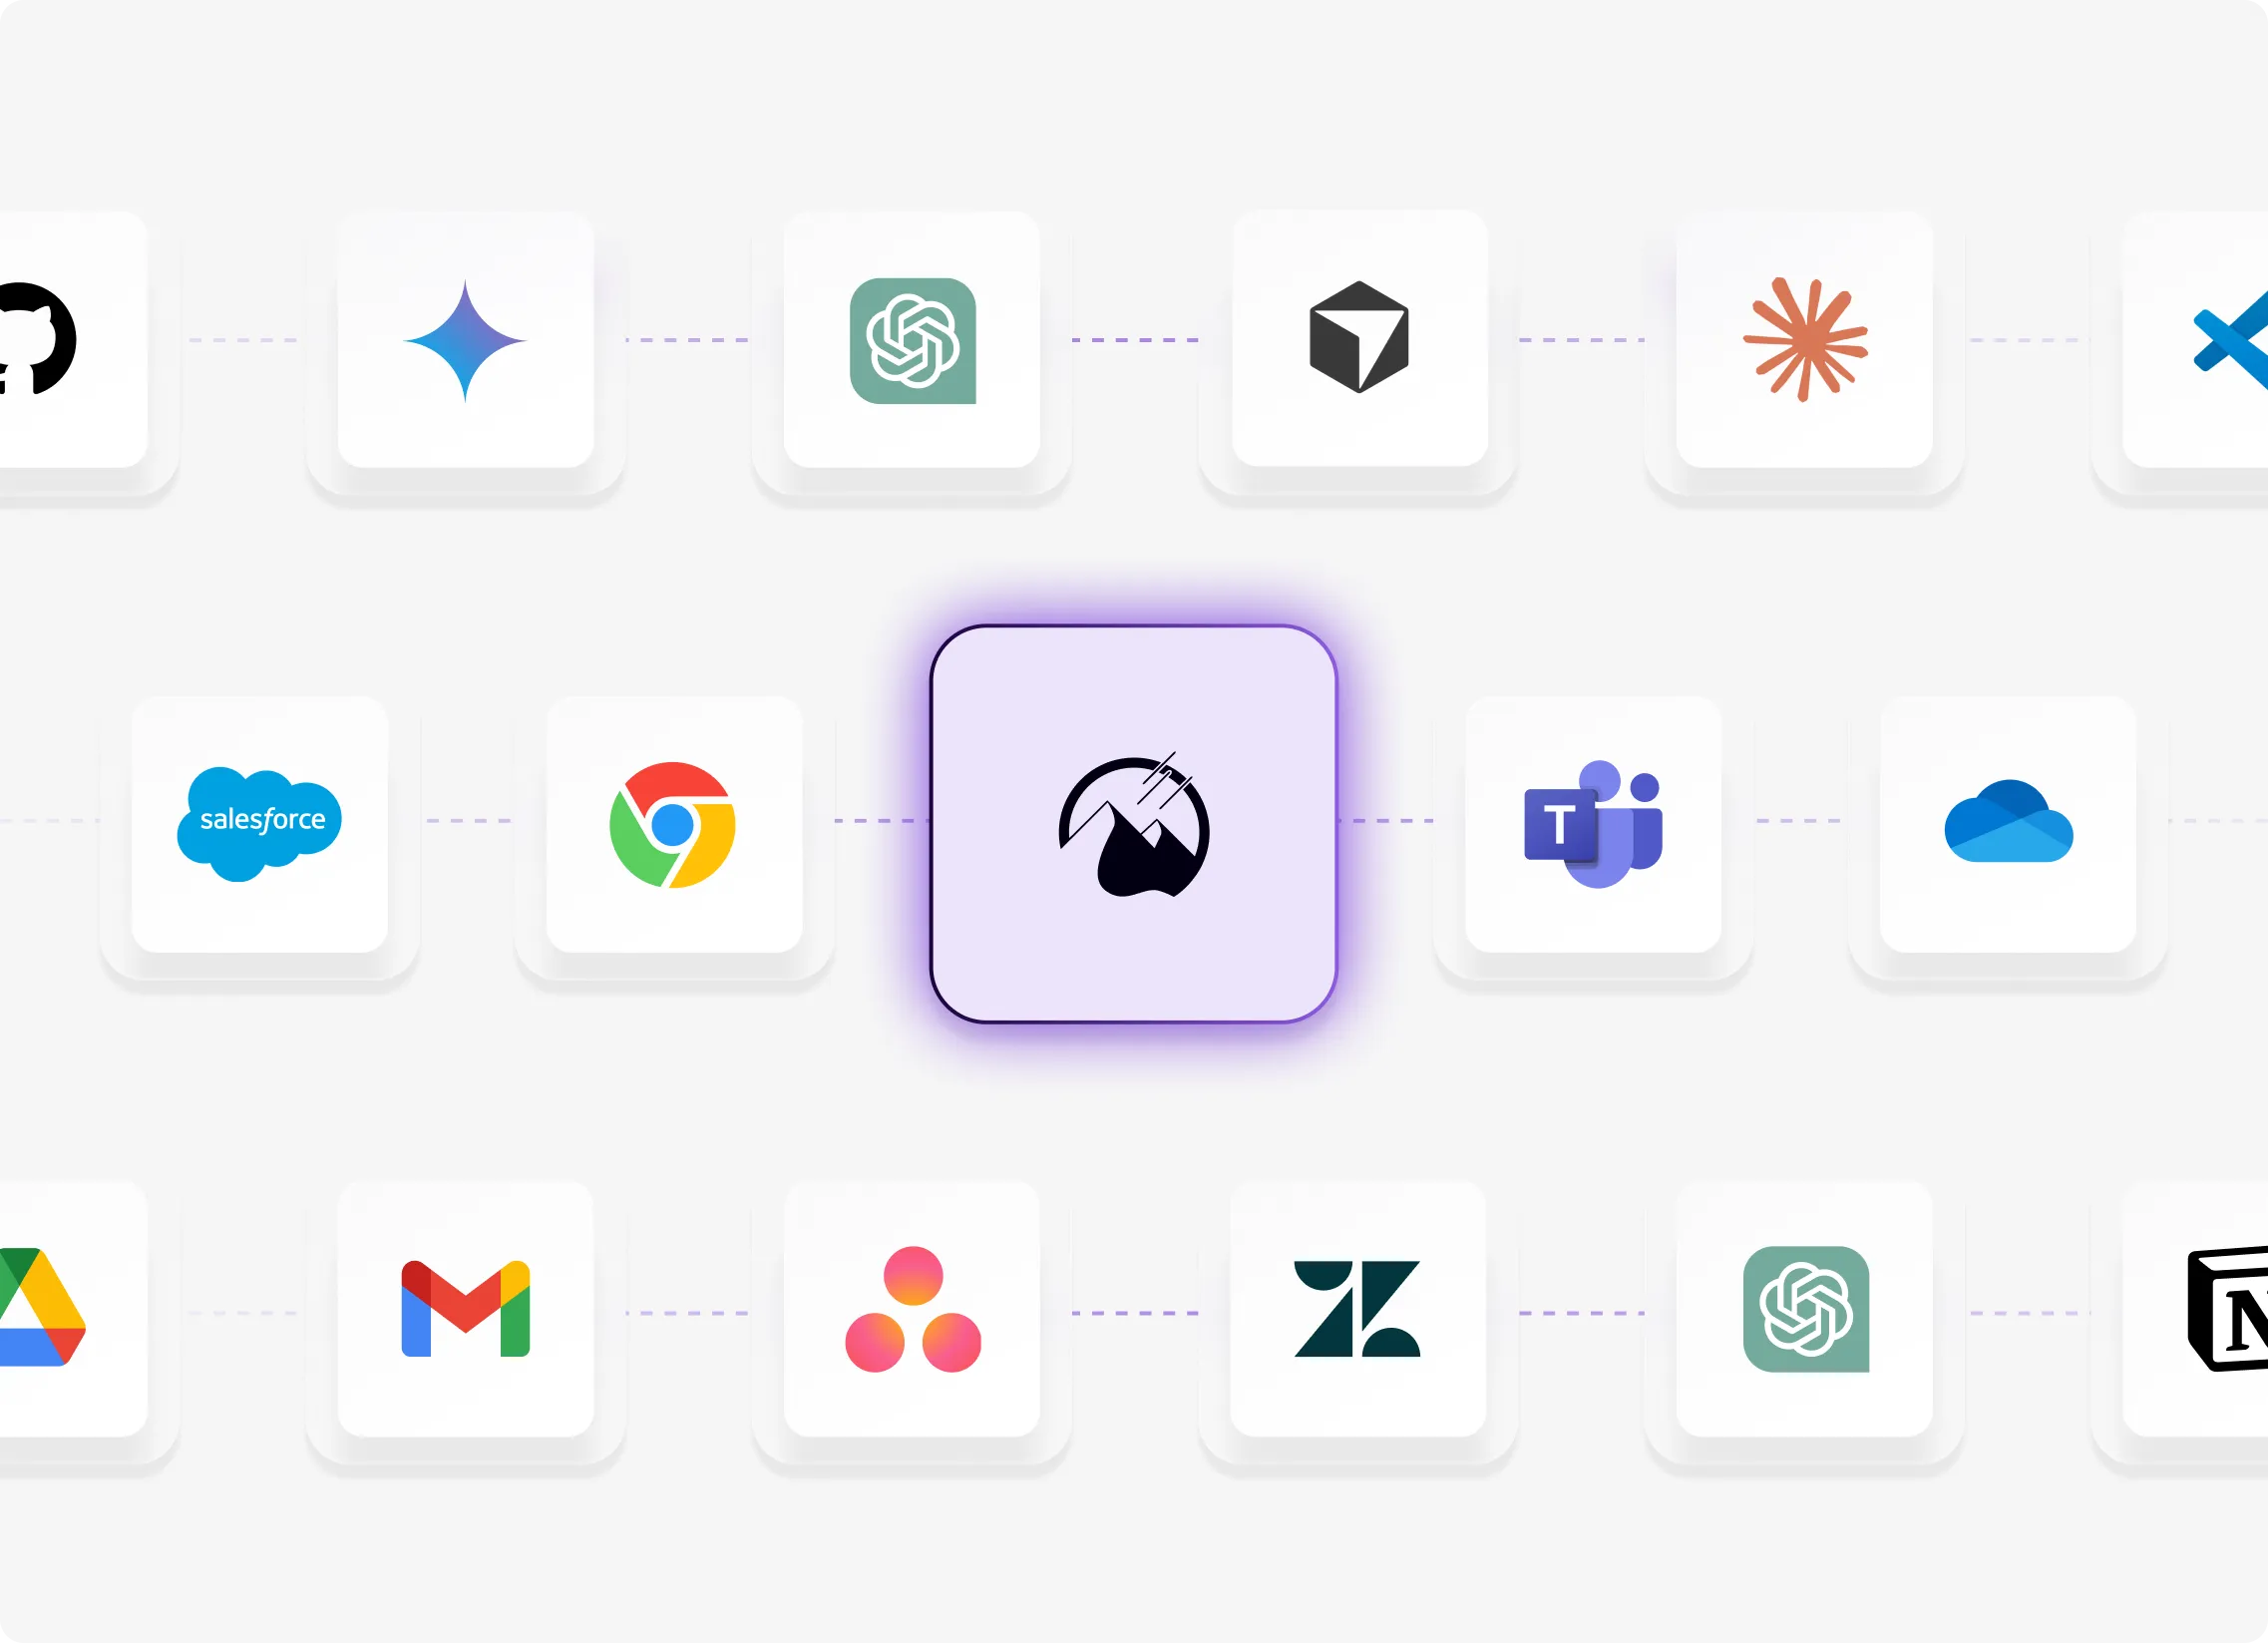
- Slack, Google Drive, Gmail, Jira, Confluence, M365 Teams, OneDrive, Exchange Online, SharePoint, Salesforce, Zendesk, Notion, GitHub
- Zero-friction deployment, no agents on the SaaS side
- Shadow AI detection - flag unapproved tools instantly
- Secure your sensitive assets within a day-ready reports for compliance teams
> connect apps=13 method=api proxies=0 elapsed=14m status=SCANNING
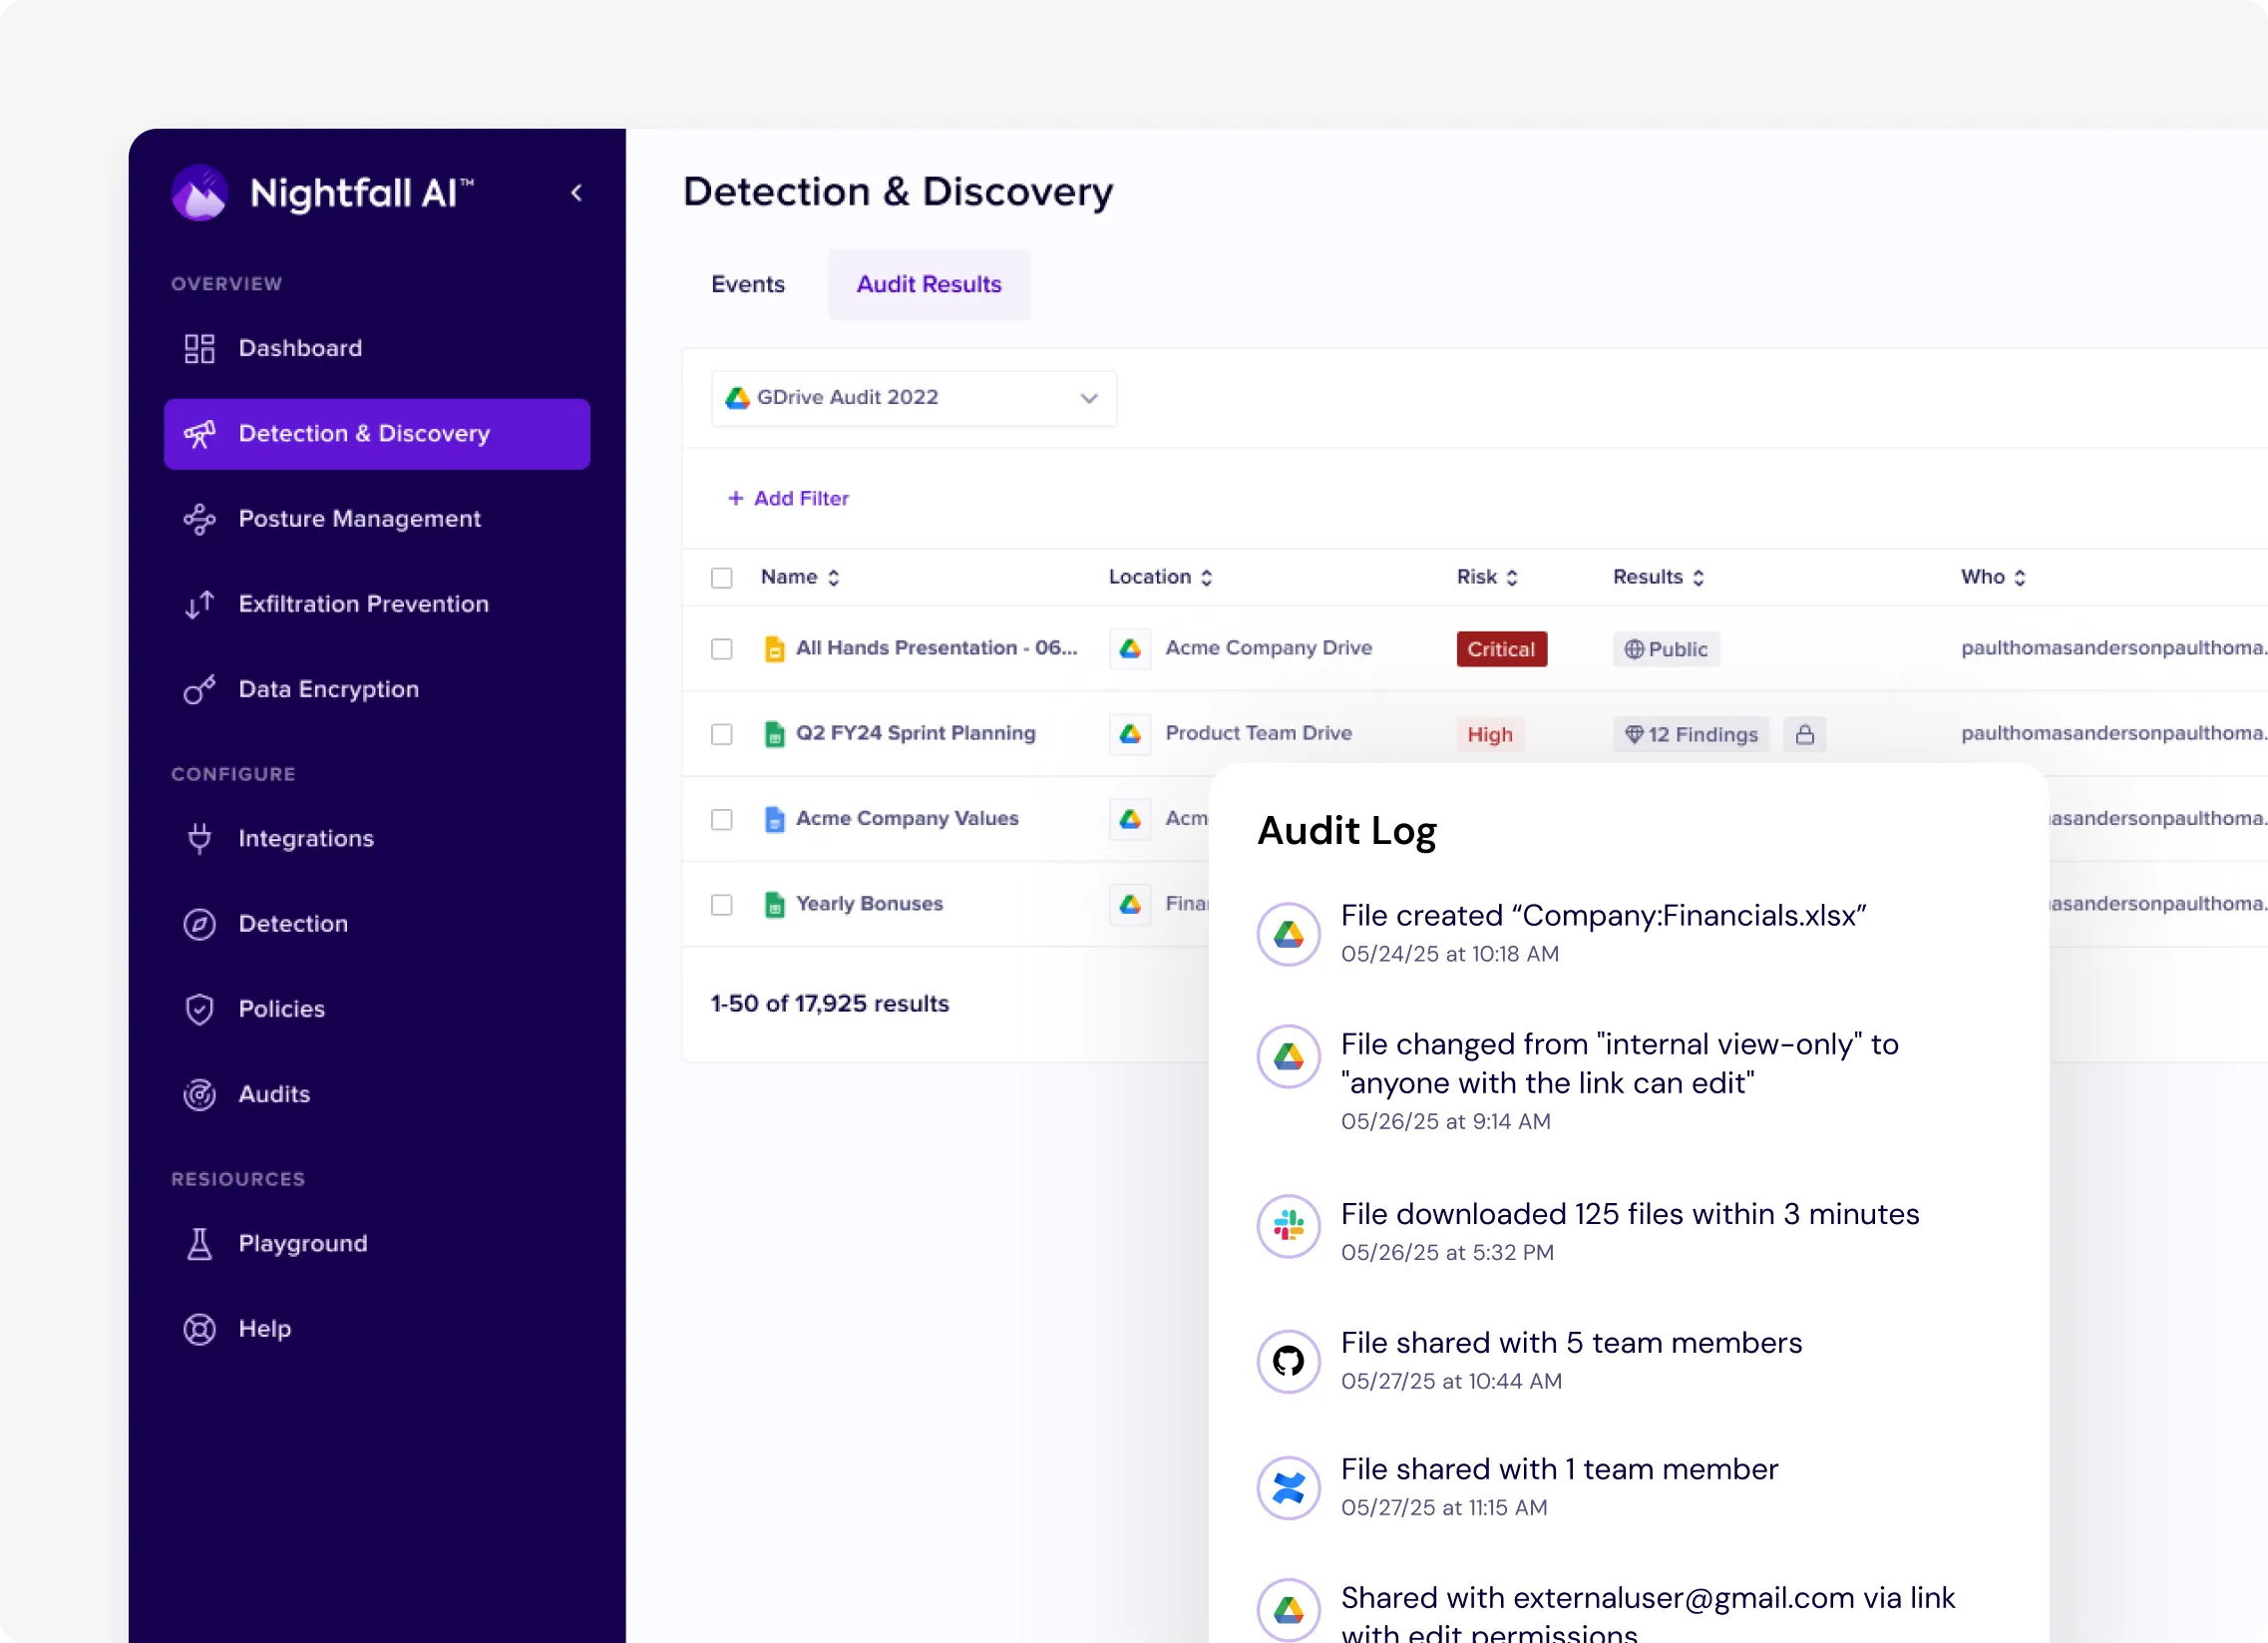
Comprehensive historical
audit
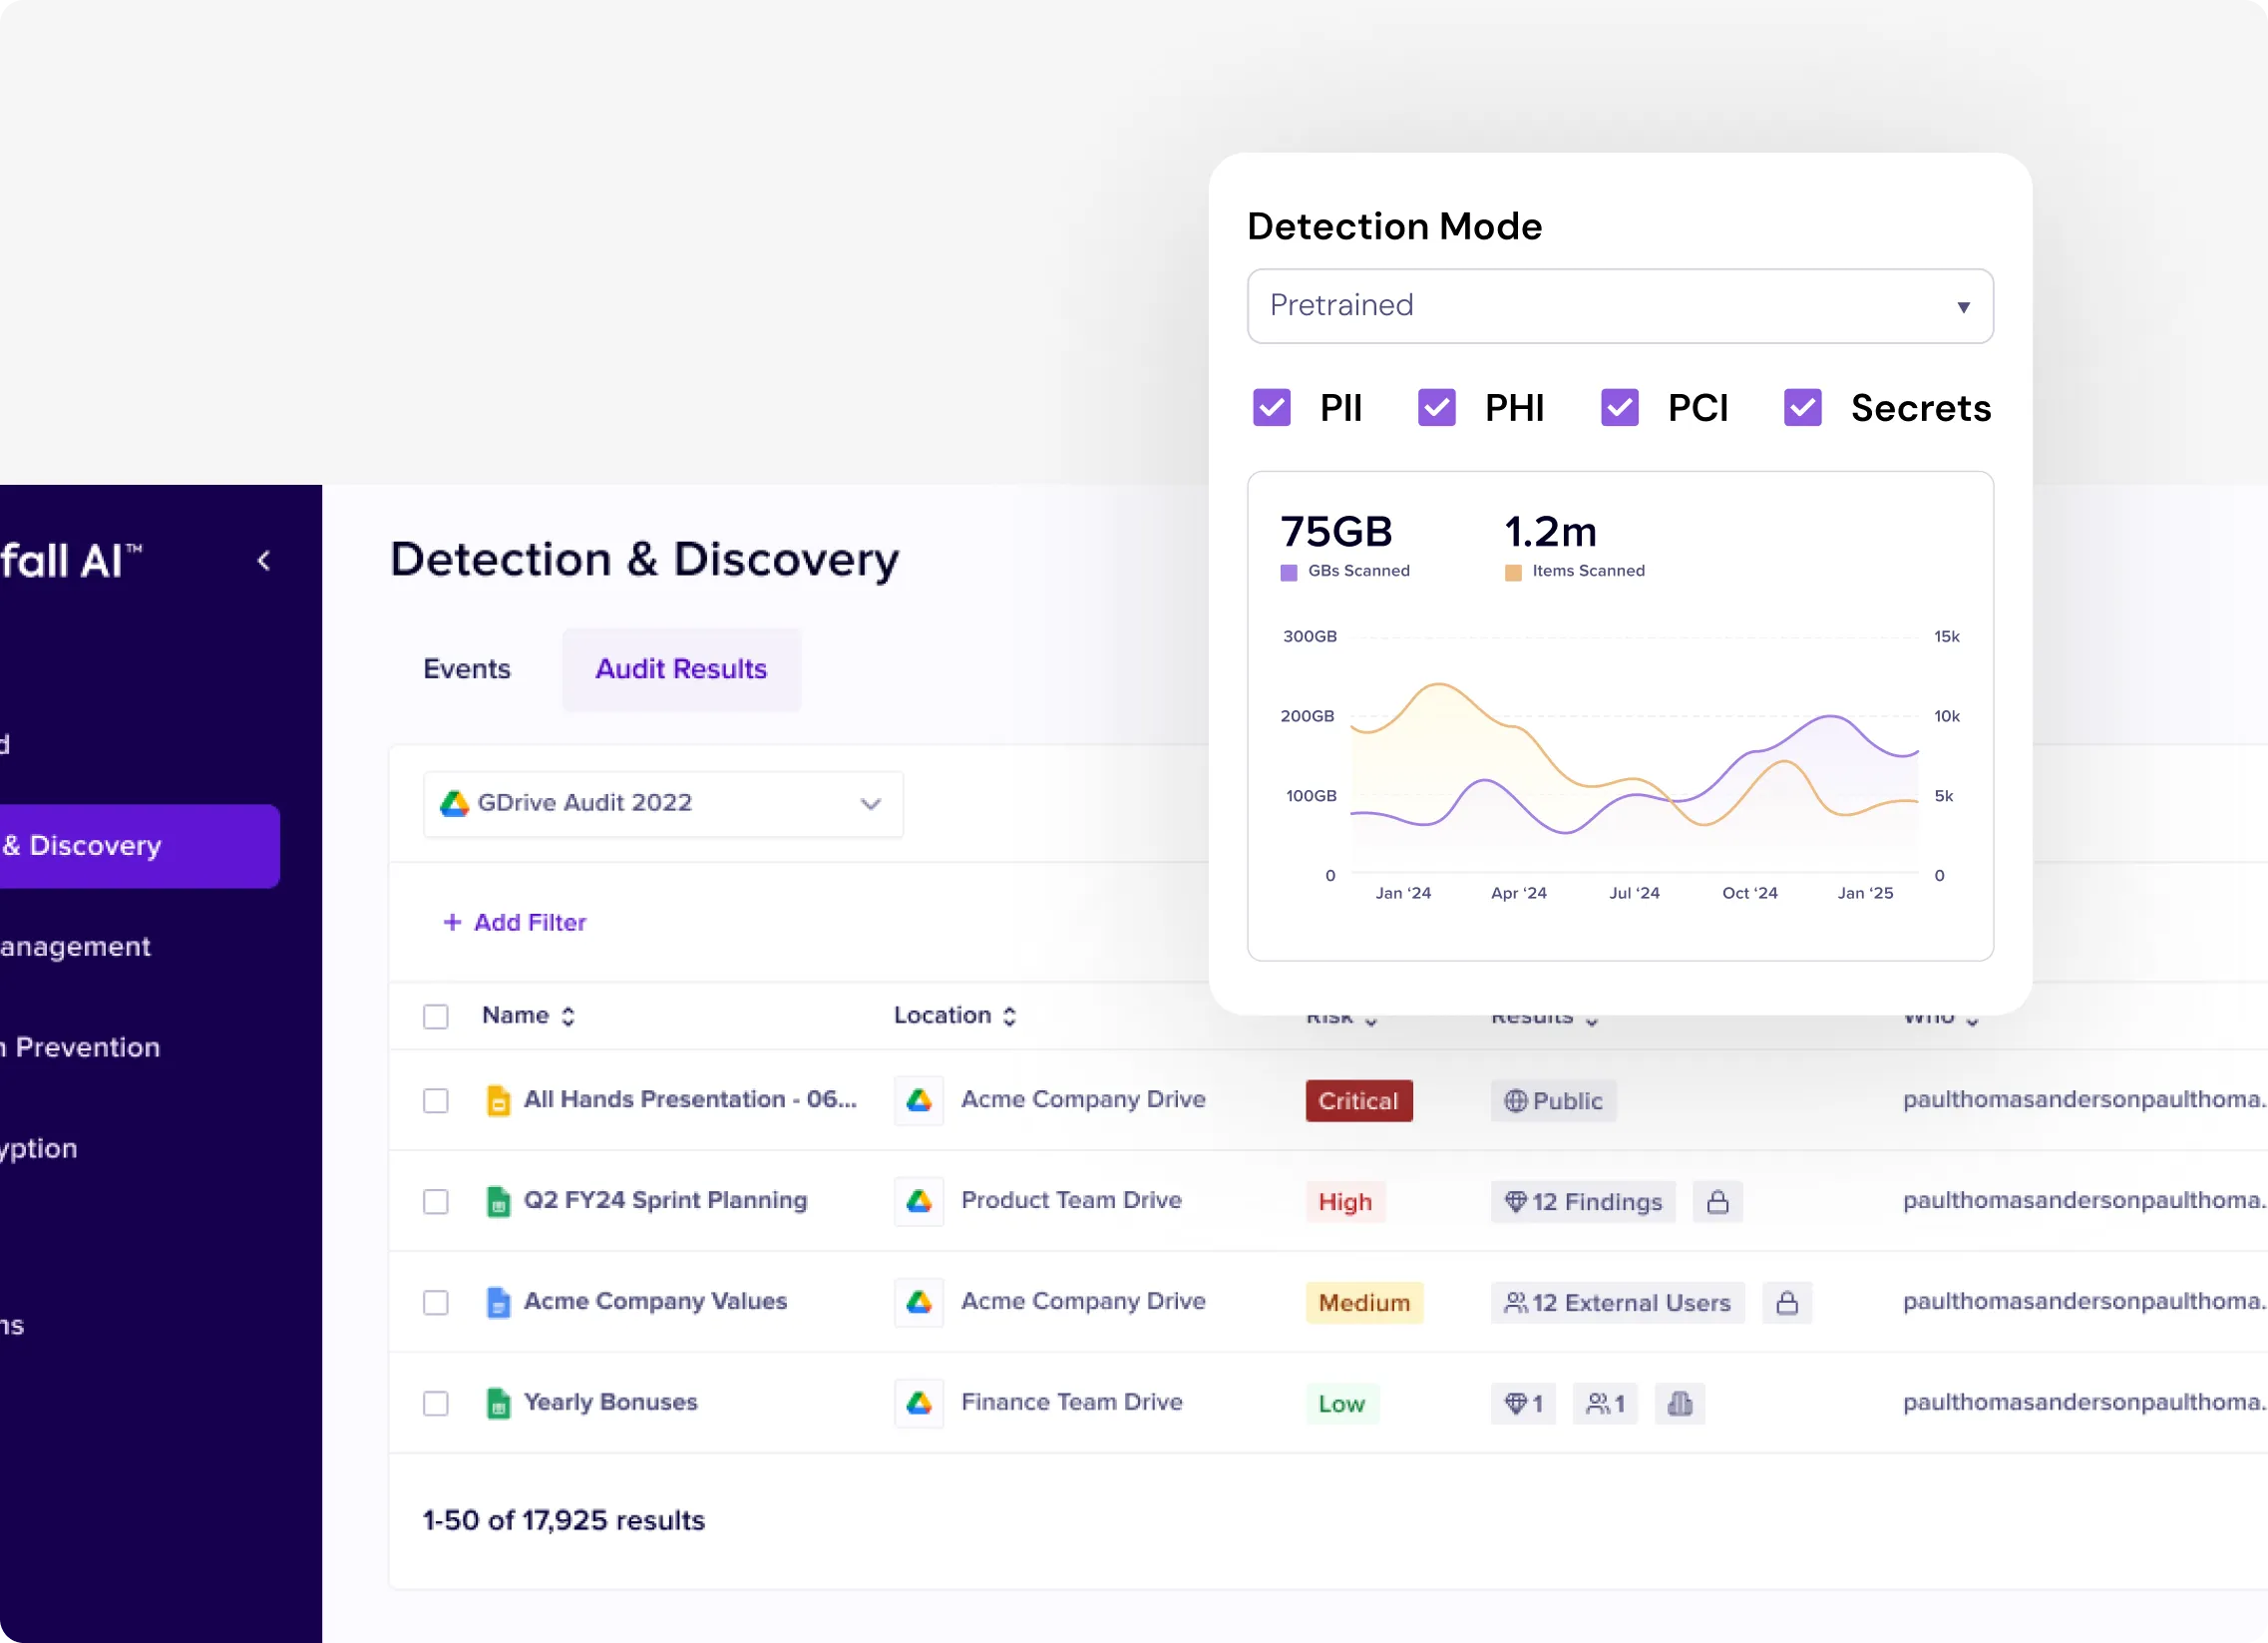
- Granular audits by date range, file age, app location, permission setting, user
- Full context of permission changes in the console
- Hours, not the months required by traditional tools
> audit scope=google_drive files=1,284,200 public_links=4,312 external_shares=18,904 ex_employee_access=2,117
AI-powered detectors, 95% precision out of the box
- Secrets validated live: API keys, JWT tokens, passwords, connection strings across tens of vendors
- Relationships between patient identifiers, conditions, and treatments, not just patterns
- Annotation workflows for true/false positives; detectors retrain on your environment automatically
> classify file="Q3_patients.xlsx" phi=2,140 pci=0 secrets=1(validated:aws) confidence=0.97 risk=HIGH(public_link)
Real-time monitoring
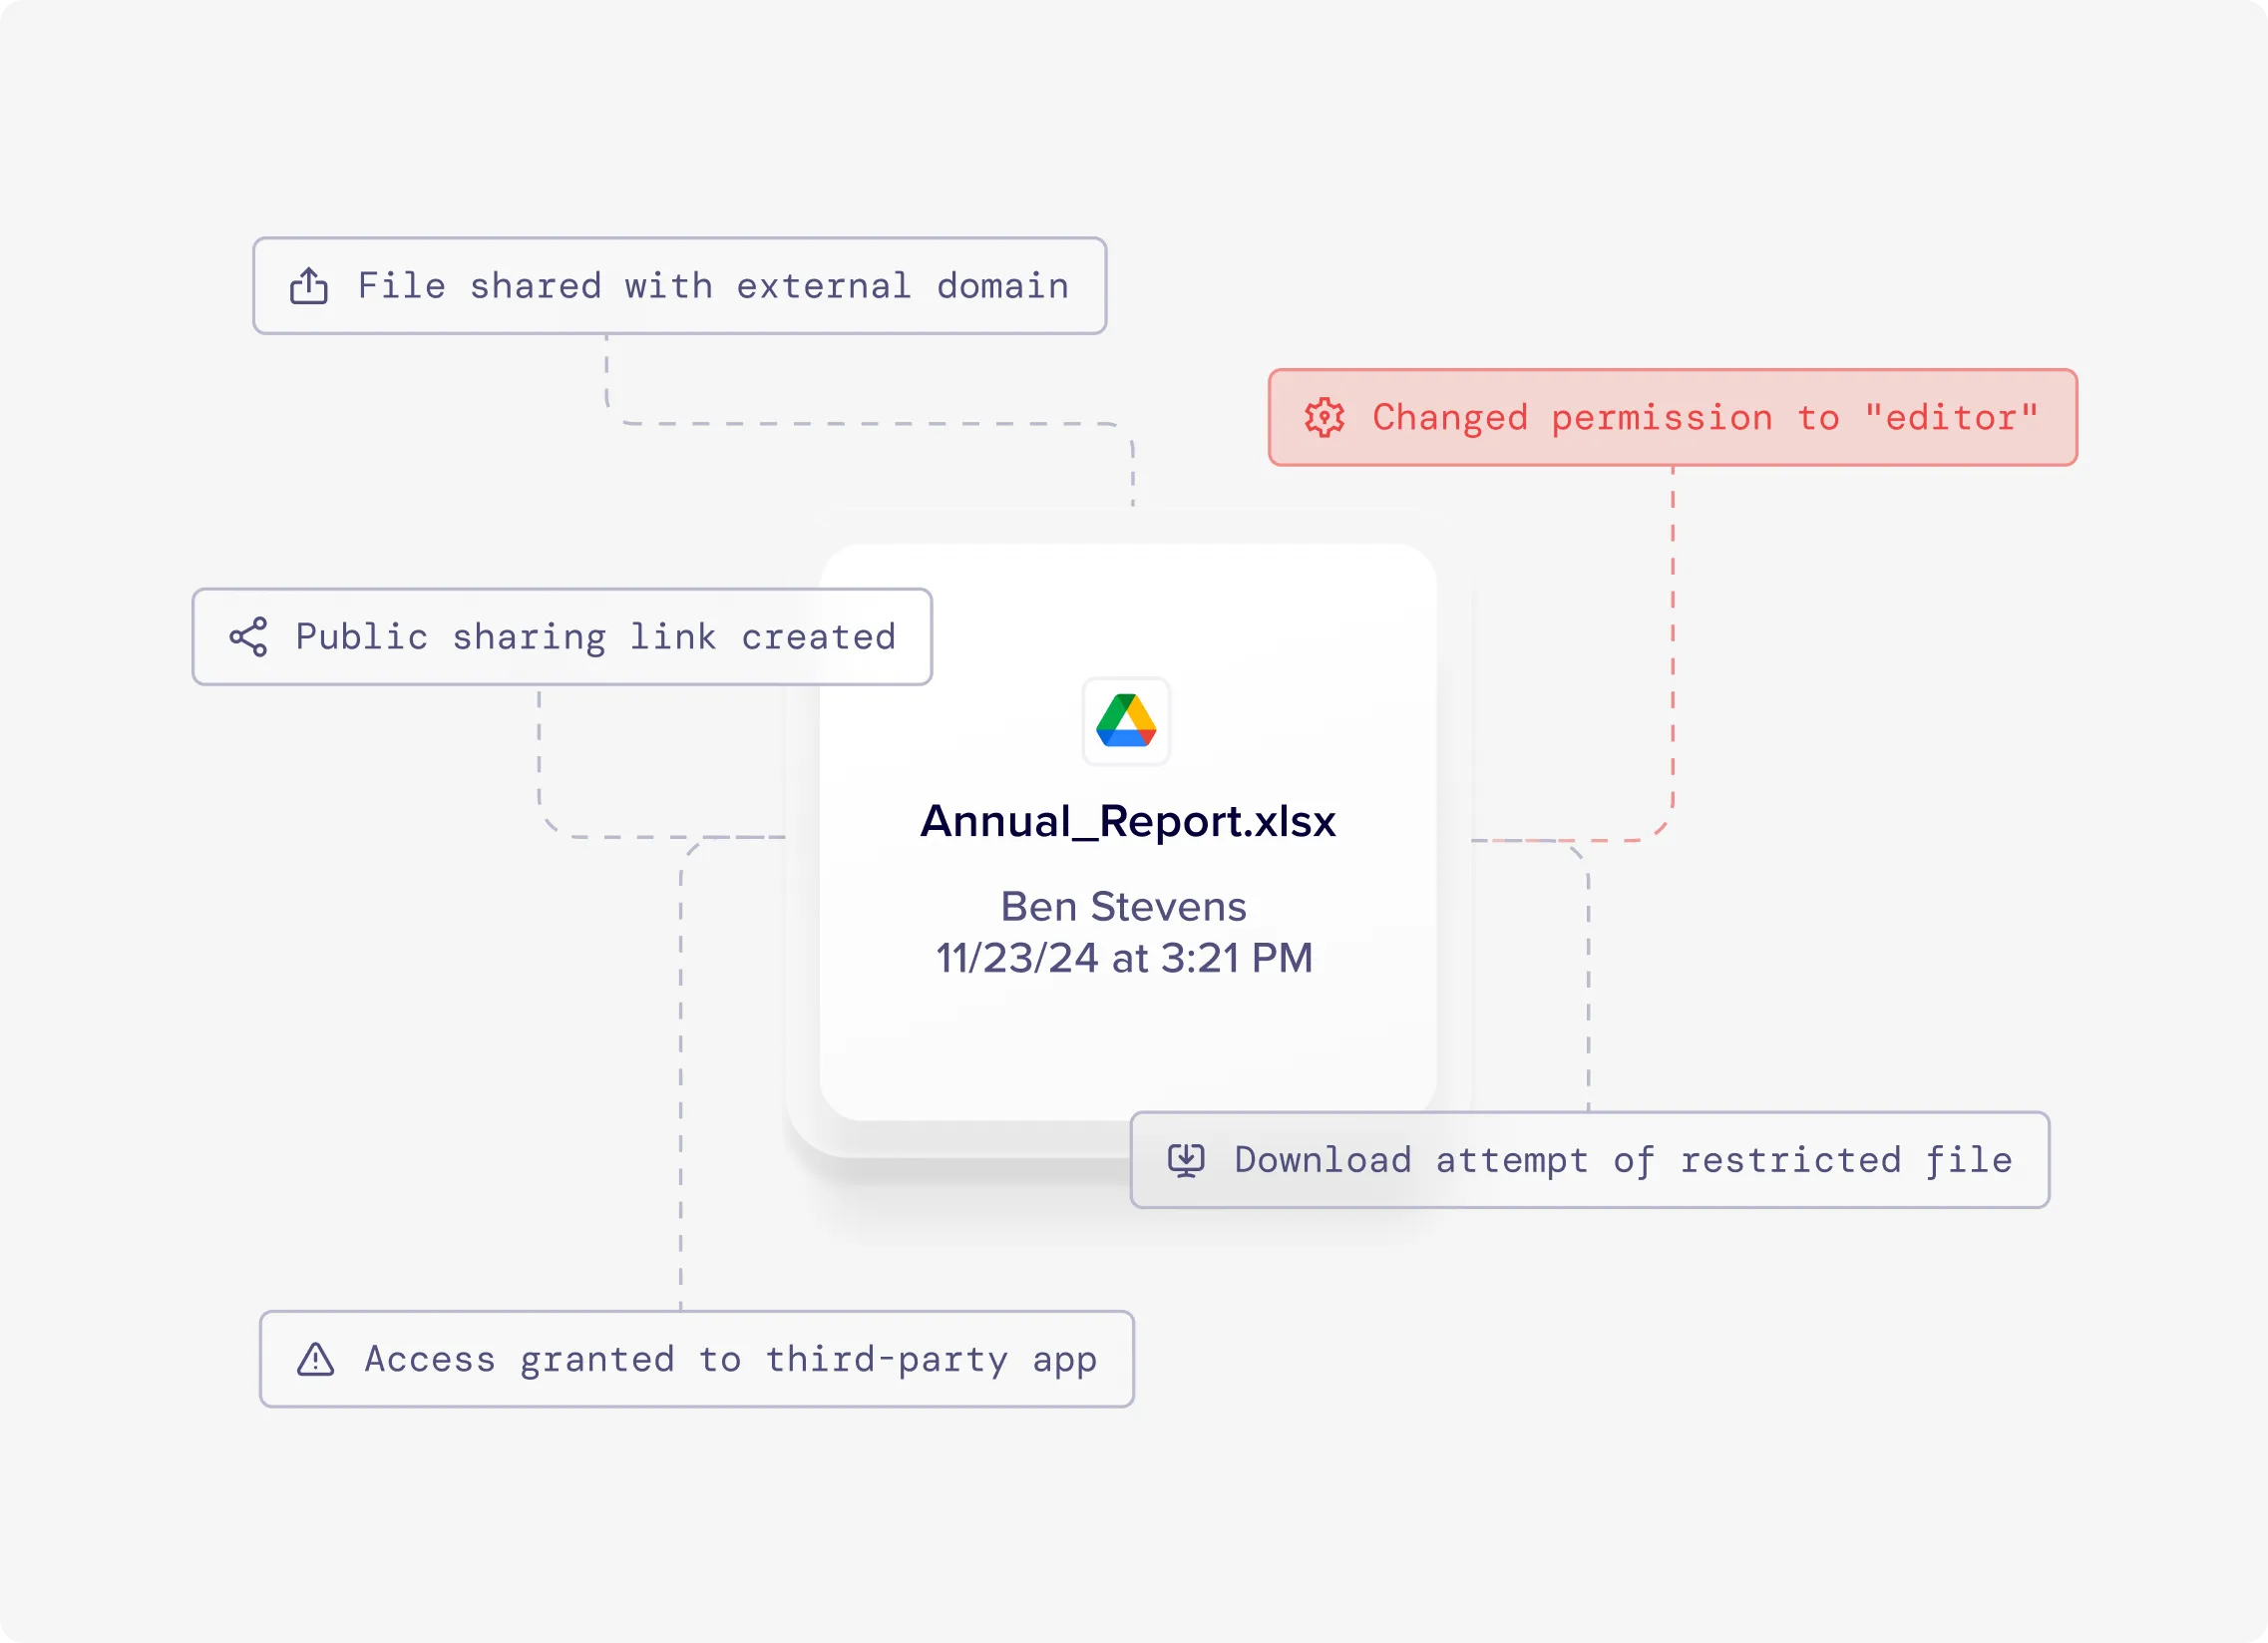
- Instant alerts on high-risk sharing changes
- Schedule delayed remediation: allow legitimate collaboration, then auto-revoke after minutes, hours, days, or weeks
- Intelligent grouping reduces alert fatigue
> monitor event=share_external file="MSA_v4.docx" to=vendor.com action=ENCRYPT revoke_at=+30d
Automated, bulk remediation
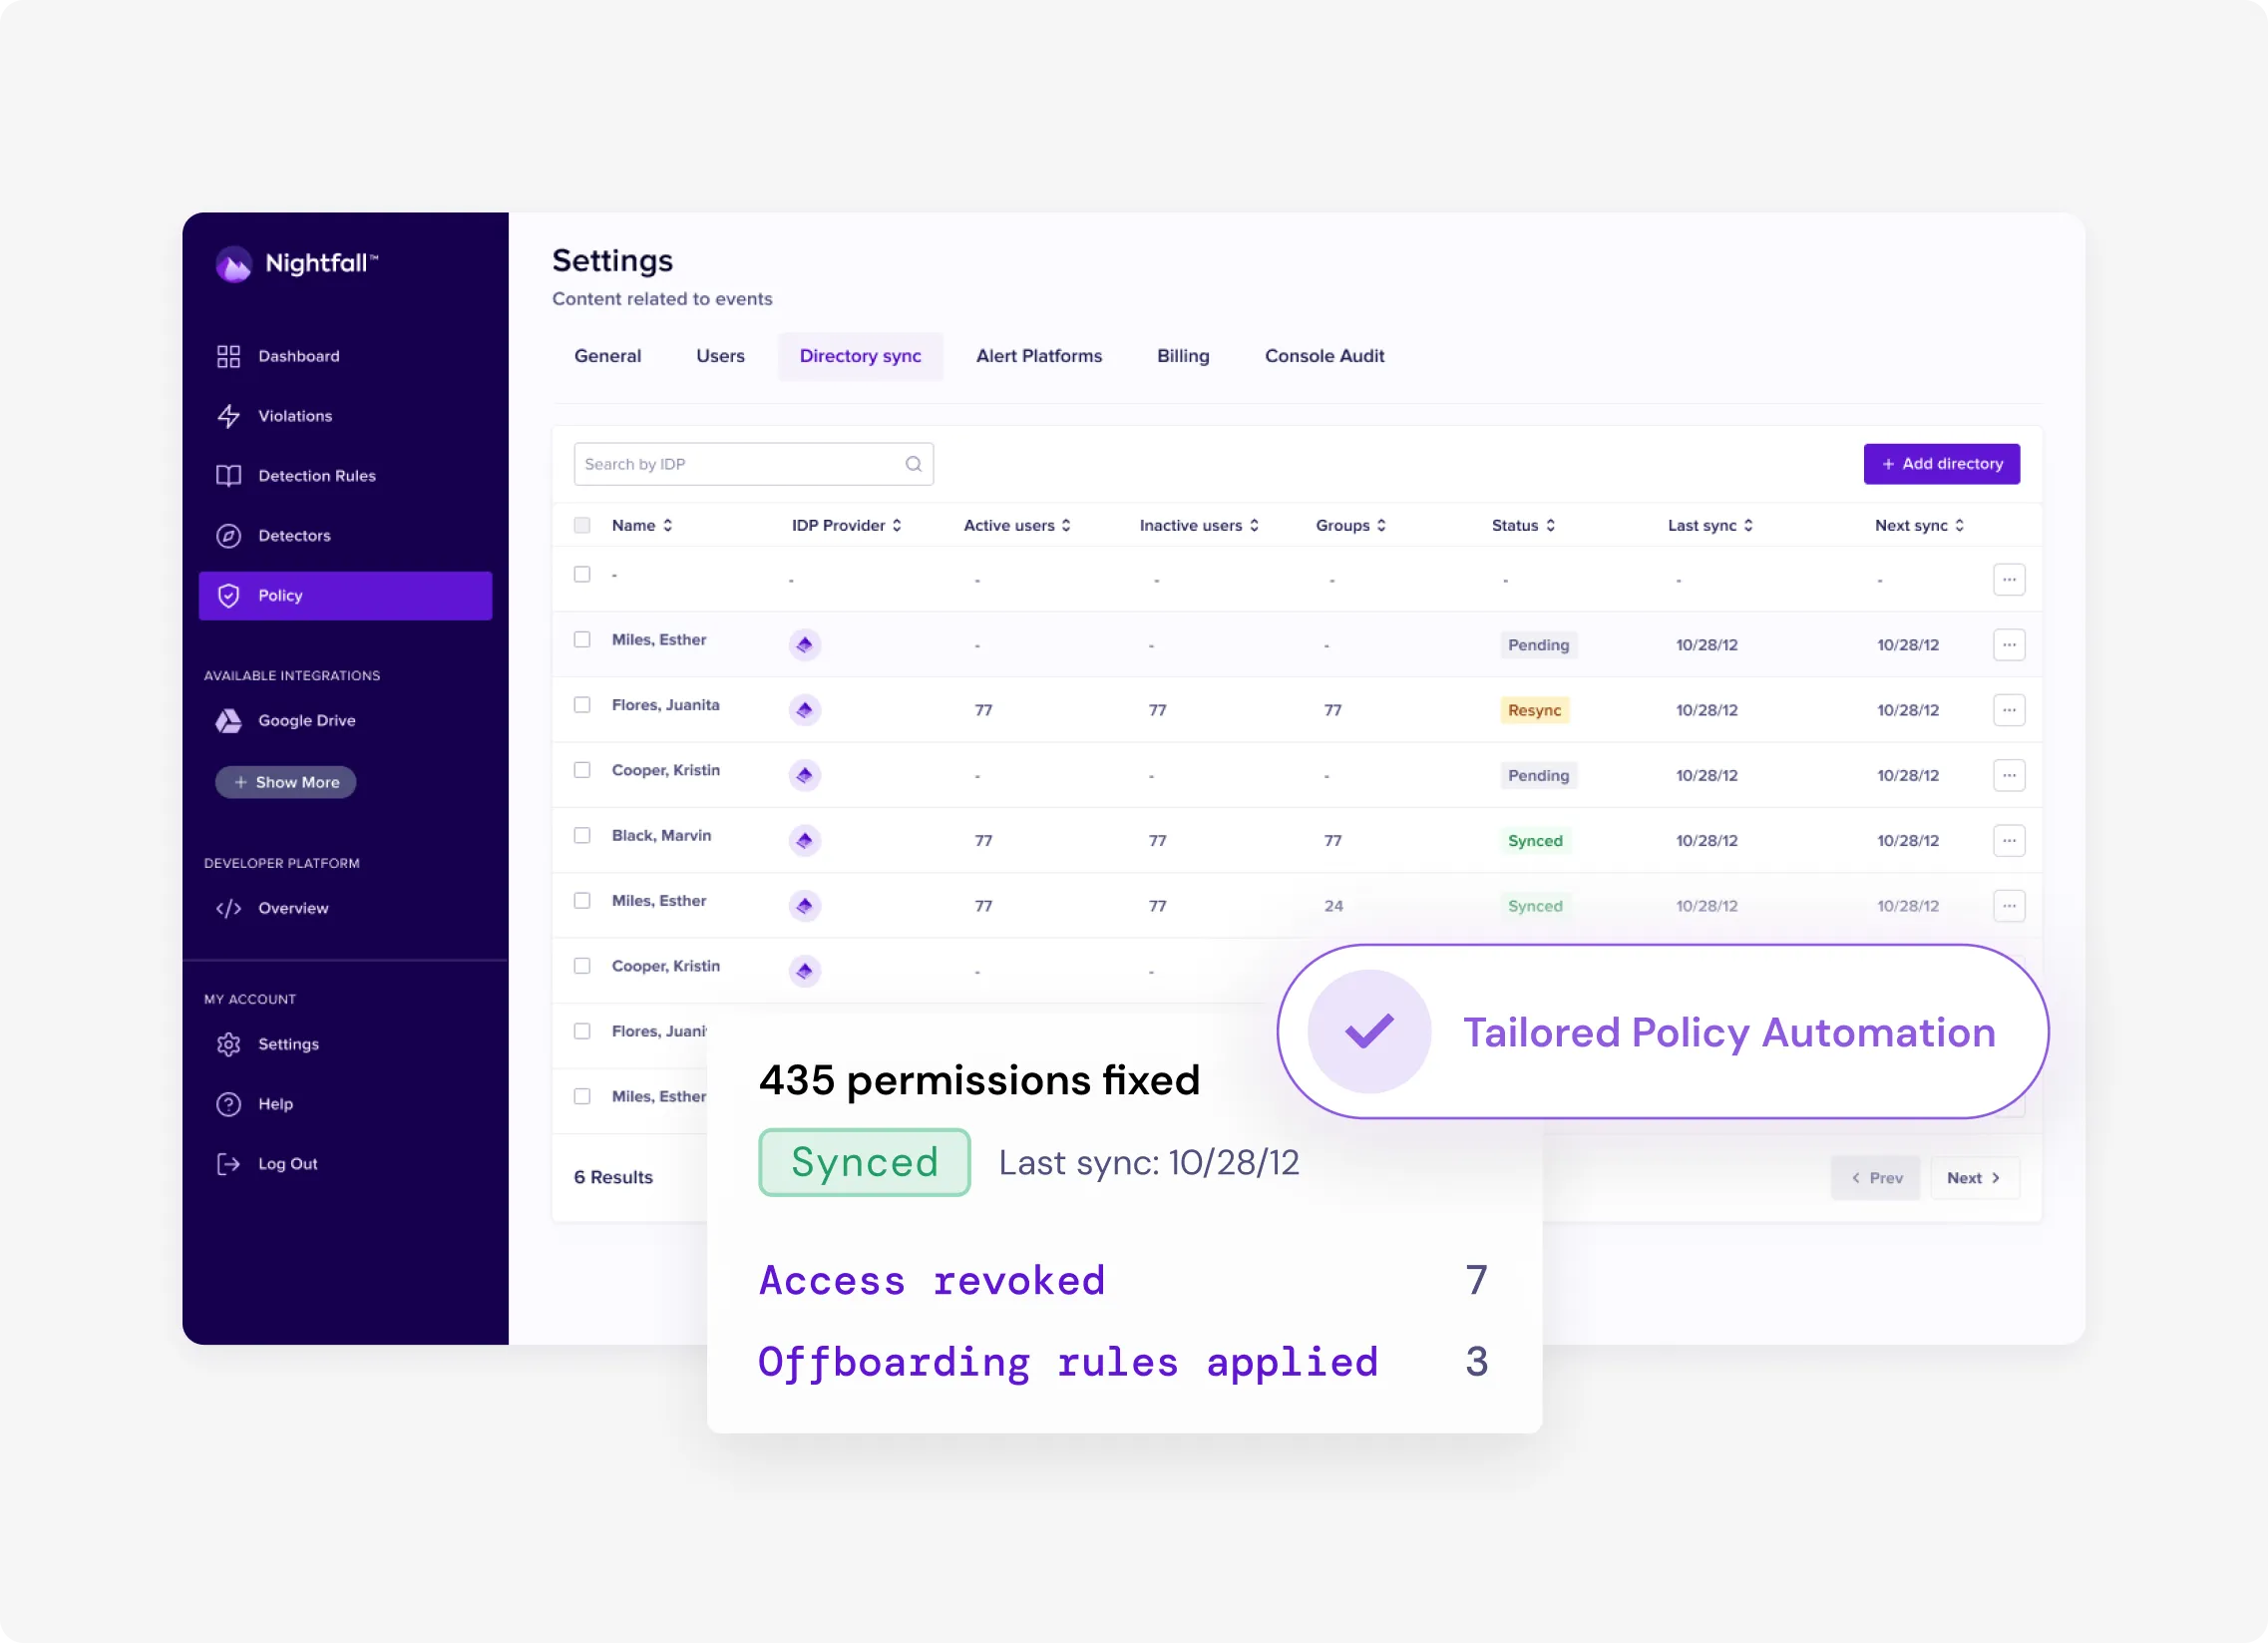
- Policies tailored to users and groups synced from Okta, Entra ID, or Google Directory
- Block, delete, redact, quarantine, encrypt, or notify by risk level
- Specialized rules for departing employees
> remediate bulk=4,312 action=public→private revoked=2,117(ex_employees) elapsed=41s tickets=jira:18
Review in the console or your SIEM/SOAR
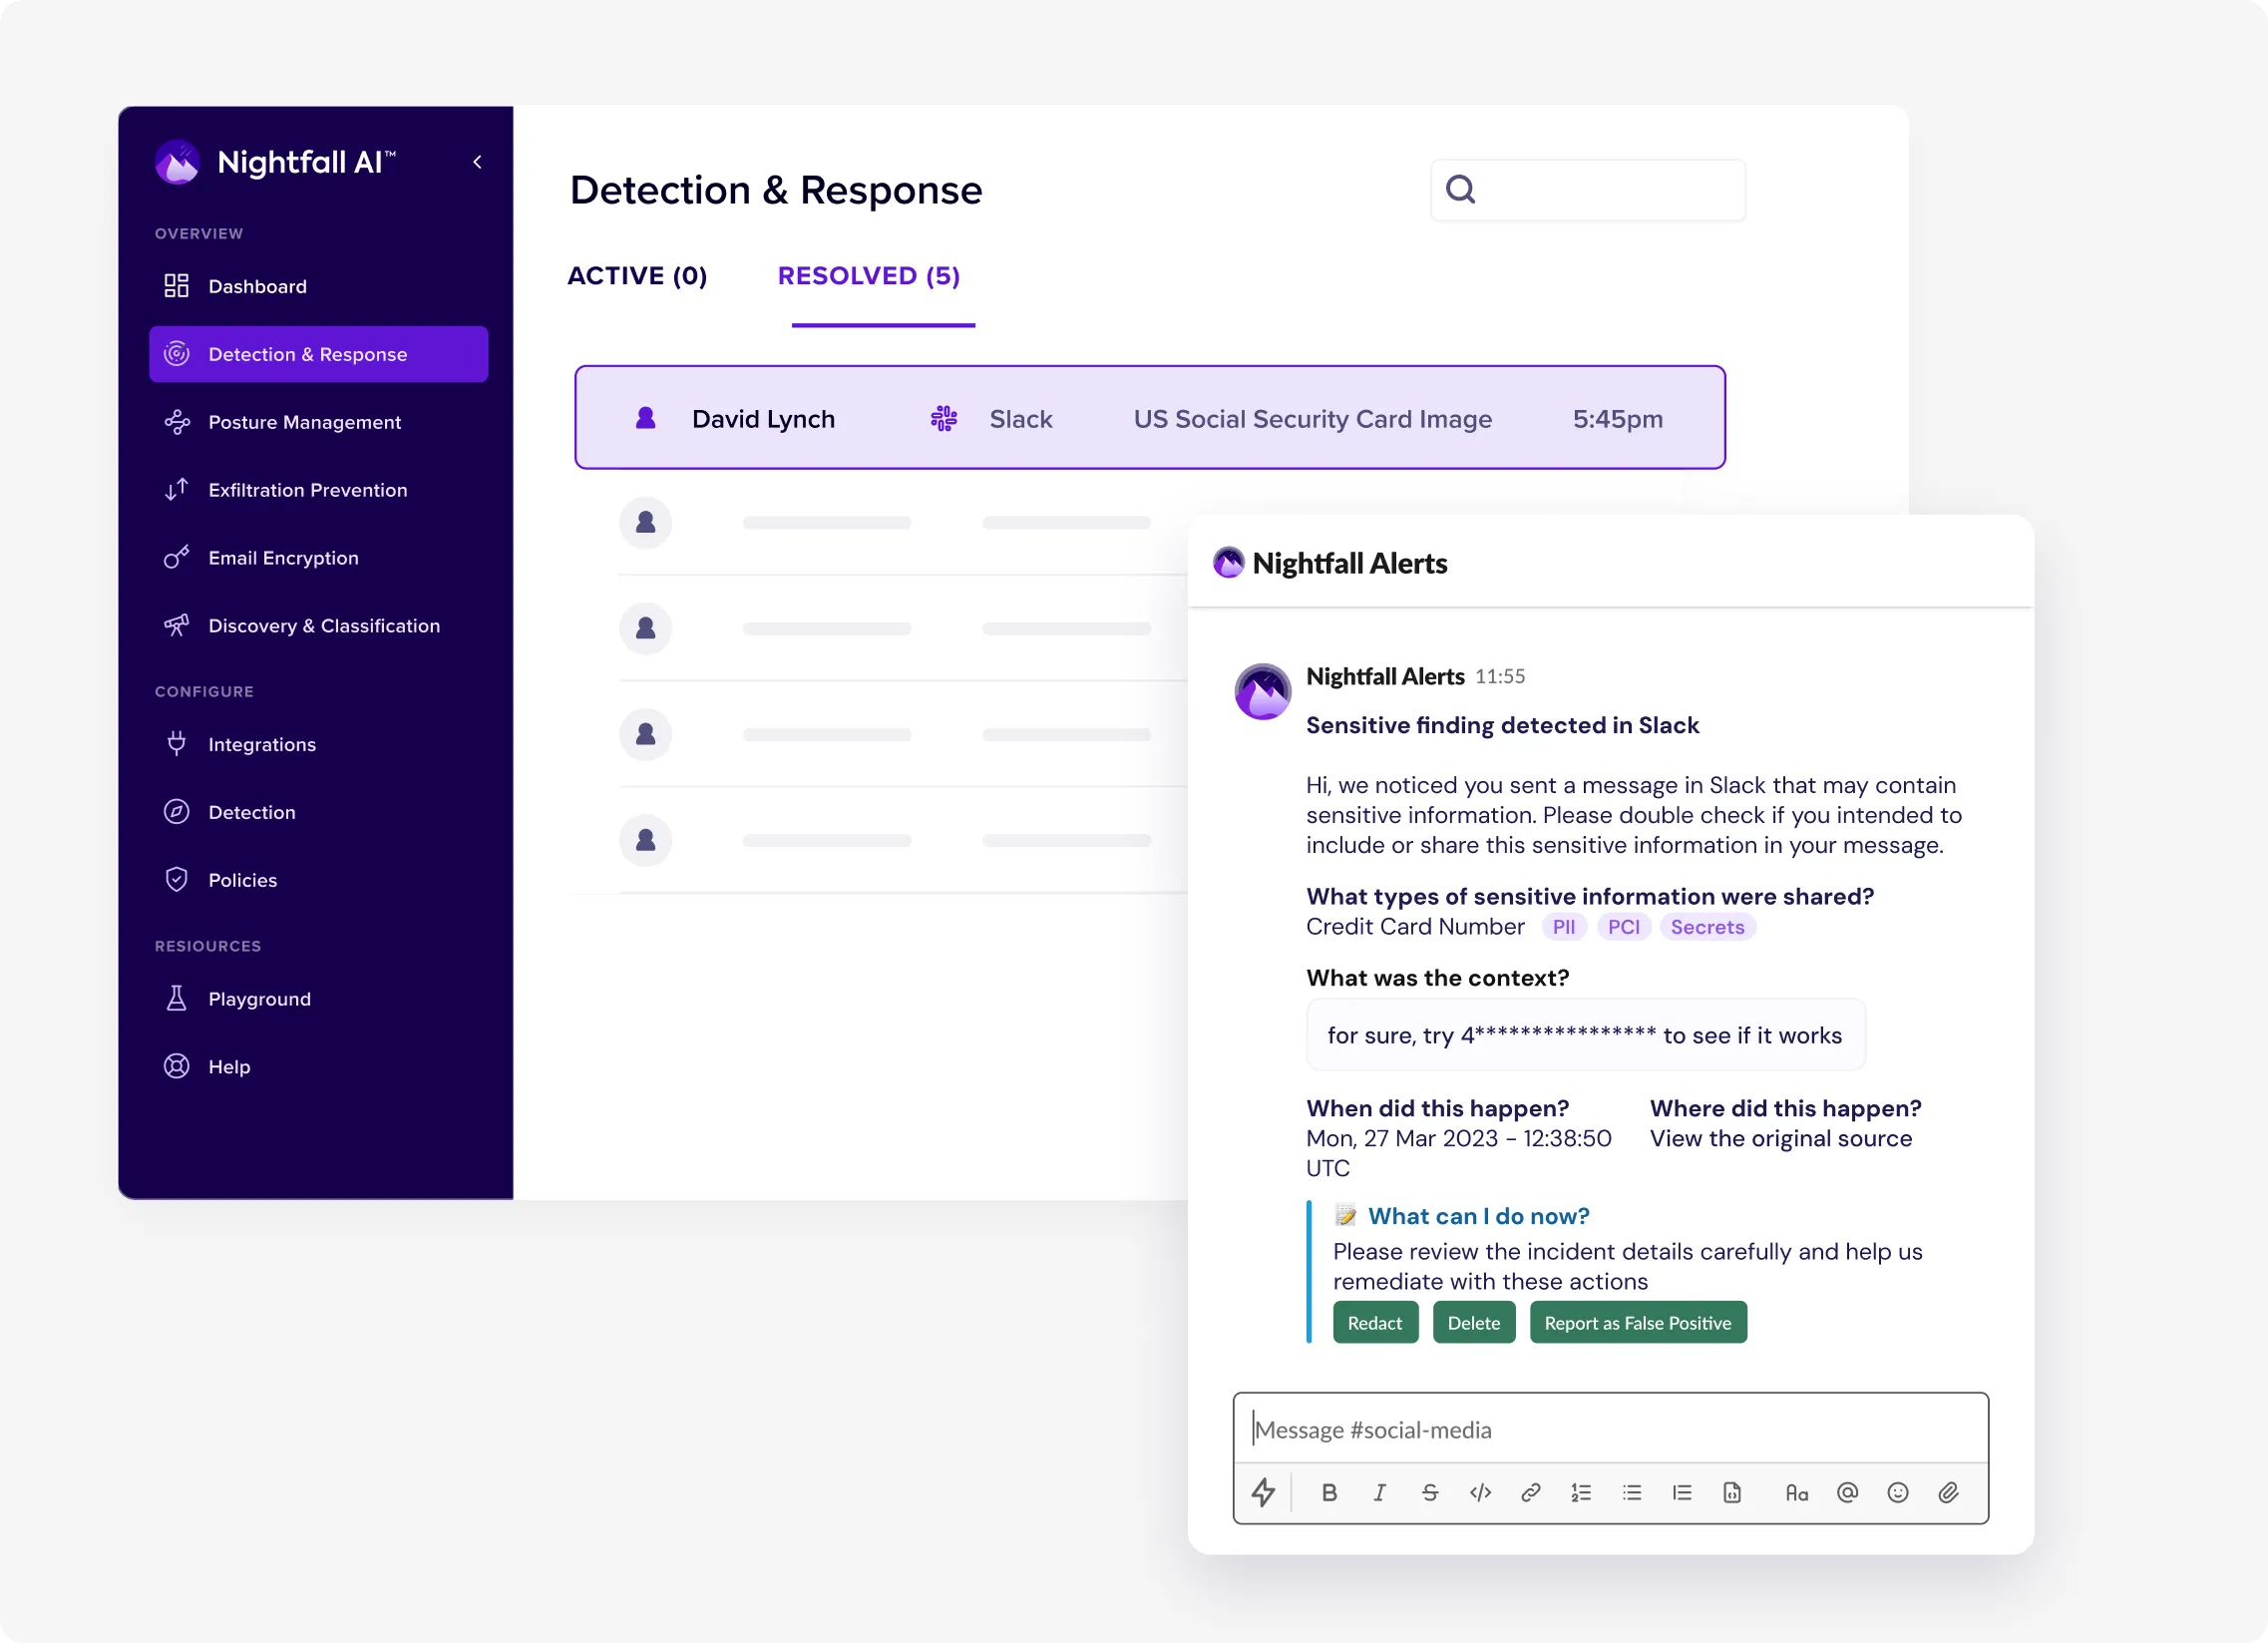
- Alerts to Slack, M365 Teams, Jira, or Email with redacted snippets, violated policy, and recommended action
- Automated Jira tickets assigned to asset owners and tracked to closure
- APIs and webhooks drive response in your existing orchestration
> alert channel=slack#secops file="Q3_patients.xlsx" owner=r.alvarez policy=PHI_public recommended=REVOKE_LINK jira=SEC-2291
Six kinds of exposure, one sweep
From public GitHub repos to Slack Connect channels, Confluence spaces to Salesforce records. Deep historical audit plus continuous real-time monitoring.
Leaked secrets and credentials

API keys, JWT tokens, passwords, and database connection strings across tens of vendors. Identified, validated, and prevented from exposure with pinpoint accuracy.
Regulated data beyond regex

High-precision detection across many dimensions of patient and customer data, including the relationships between identifiers, conditions, and treatments.
Files shared with everyone

Every document with a public or company-wide link. Flip public to private across entire shared drives in seconds.
Shares to unmanaged accounts

Sensitive documents routinely shared to Gmail and other personal addresses. Instant visibility, business-justification prompts, automated revocation.
Access that outlived the employee

Automatically identify and revoke document access for departed employees. Specialized rules for departing staff that keep them productive until the last day.
Vendor and contractor sprawl

Monitor and manage document access for vendors, contractors, and partners. Schedule revocation for when the collaboration ends: minutes, days, or weeks later.
The response matches the risk
AI risk scoring reads context: a document in a public location scores higher than the same file in a private one. Policies tailored to users, groups synced from Okta, Entra ID, or Google Directory, and specific app locations apply the right action without interrupting legitimate work.
Employees stay in the loop: contextual alerts explain what was caught, self-remediation lets them fix it, and external shares prompt for business justification.
Block · delete · redact · quarantine
Public link to a file with 2,100 customer records → link revoked, owner notified, Jira ticket opened.
Encrypt · require justification
Contract shared to a vendor domain → encrypted, sender asked for business justification, revocation scheduled for 30 days.
Monitor · notify · coach
Employee’s own payslip in a private Drive folder → logged, no alert, Human Firewall tip on safer storage.
Built-in DLP vs. Nightfall
| CASB / SASE / app-native DLP | Nightfall | |
|---|---|---|
| Detection | Basic pattern matching and regex; misses context | Pre-trained LLM and CV models, 95% precision out of the box |
| False positives | 75–95% of alerts; extensive manual tuning | Context and intent aware; detectors retrain on your feedback |
| Coverage | Can’t centralize across critical SaaS apps | 13+ apps via API, one console, historical audit + real time |
| Remediation | One file at a time; 12+ hours a week by hand | Thousands of permissions fixed in a few clicks; scheduled revocation |
| Deployment | Gateways, proxies, single points of failure | API-based, minutes to connect, secured within a day |
See every exposure in your SaaS stack within a day
Tell us a little about yourself and we’ll connect you with a Nightfall expert who can share more about the product and answer any questions you have.
- A 30-minute call
- Tailored to your stack
- No slideware

Not ready for a demo? Read the 2026 AI Agent Risk & Action Report →