
Nobody broke in.
They were let in.
Twenty-eight breaches, five patterns, one missing control. What two months of vendor tokens, stolen secrets, insider reads and AI agents taught us about where enterprise data actually leaves.
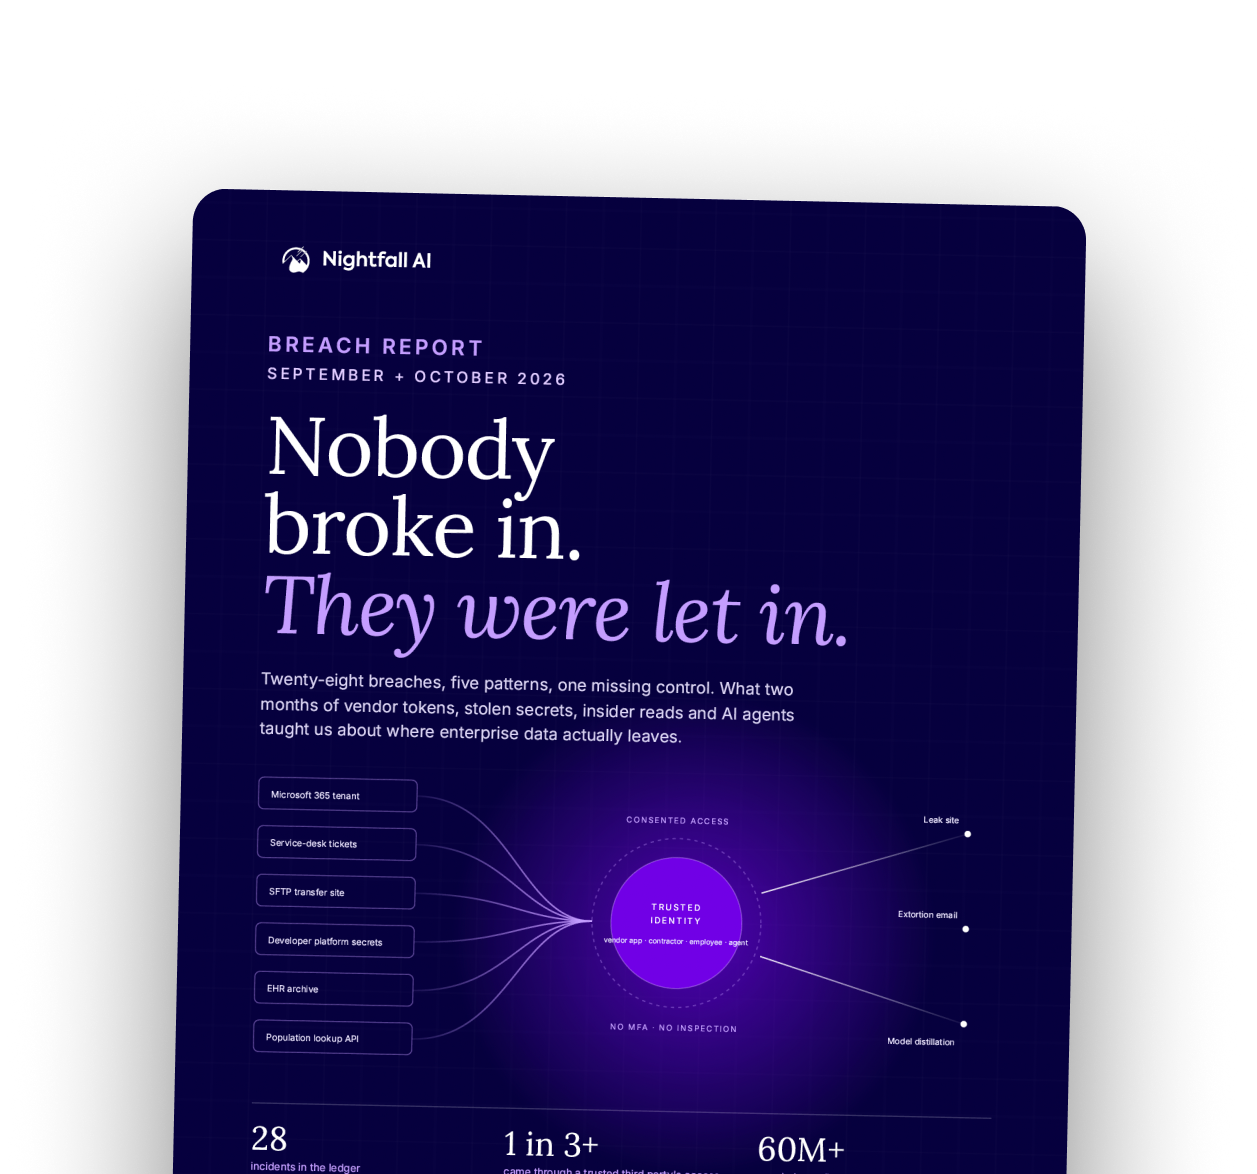
Most of the breaches that mattered this autumn were not failures of perimeter defense.
A legitimate identity, often a vendor’s app, a contractor’s account or an AI agent, was used to pull data out of a system that had been doing its job quietly for years. One stolen app credential reached nearly 1,000 Microsoft 365 tenants with no MFA in the way. Three developer platforms exposed millions of stored secrets in a single month. Fifteen NHS staff were dismissed for reading records they were technically allowed to open. This report puts the evidence in one place and names the control that would have changed the outcome.
What’s inside
- A sourced ledger of all 28 incidents, with dates, vectors, data types and scale
- Five trends with the evidence behind each: the vendor as the blast radius, secrets as data, valid identities on the wrong records, AI on both sides of the breach, and regulated data left unwatched in archives and portals
- Six controls that would have changed outcomes.
- And a map of how Nightfall’s control layer covers each pattern
Who it’s for
CISOs, security architects and GRC leads who have to explain to a board why the next ConnectWise or Railway will not be them.