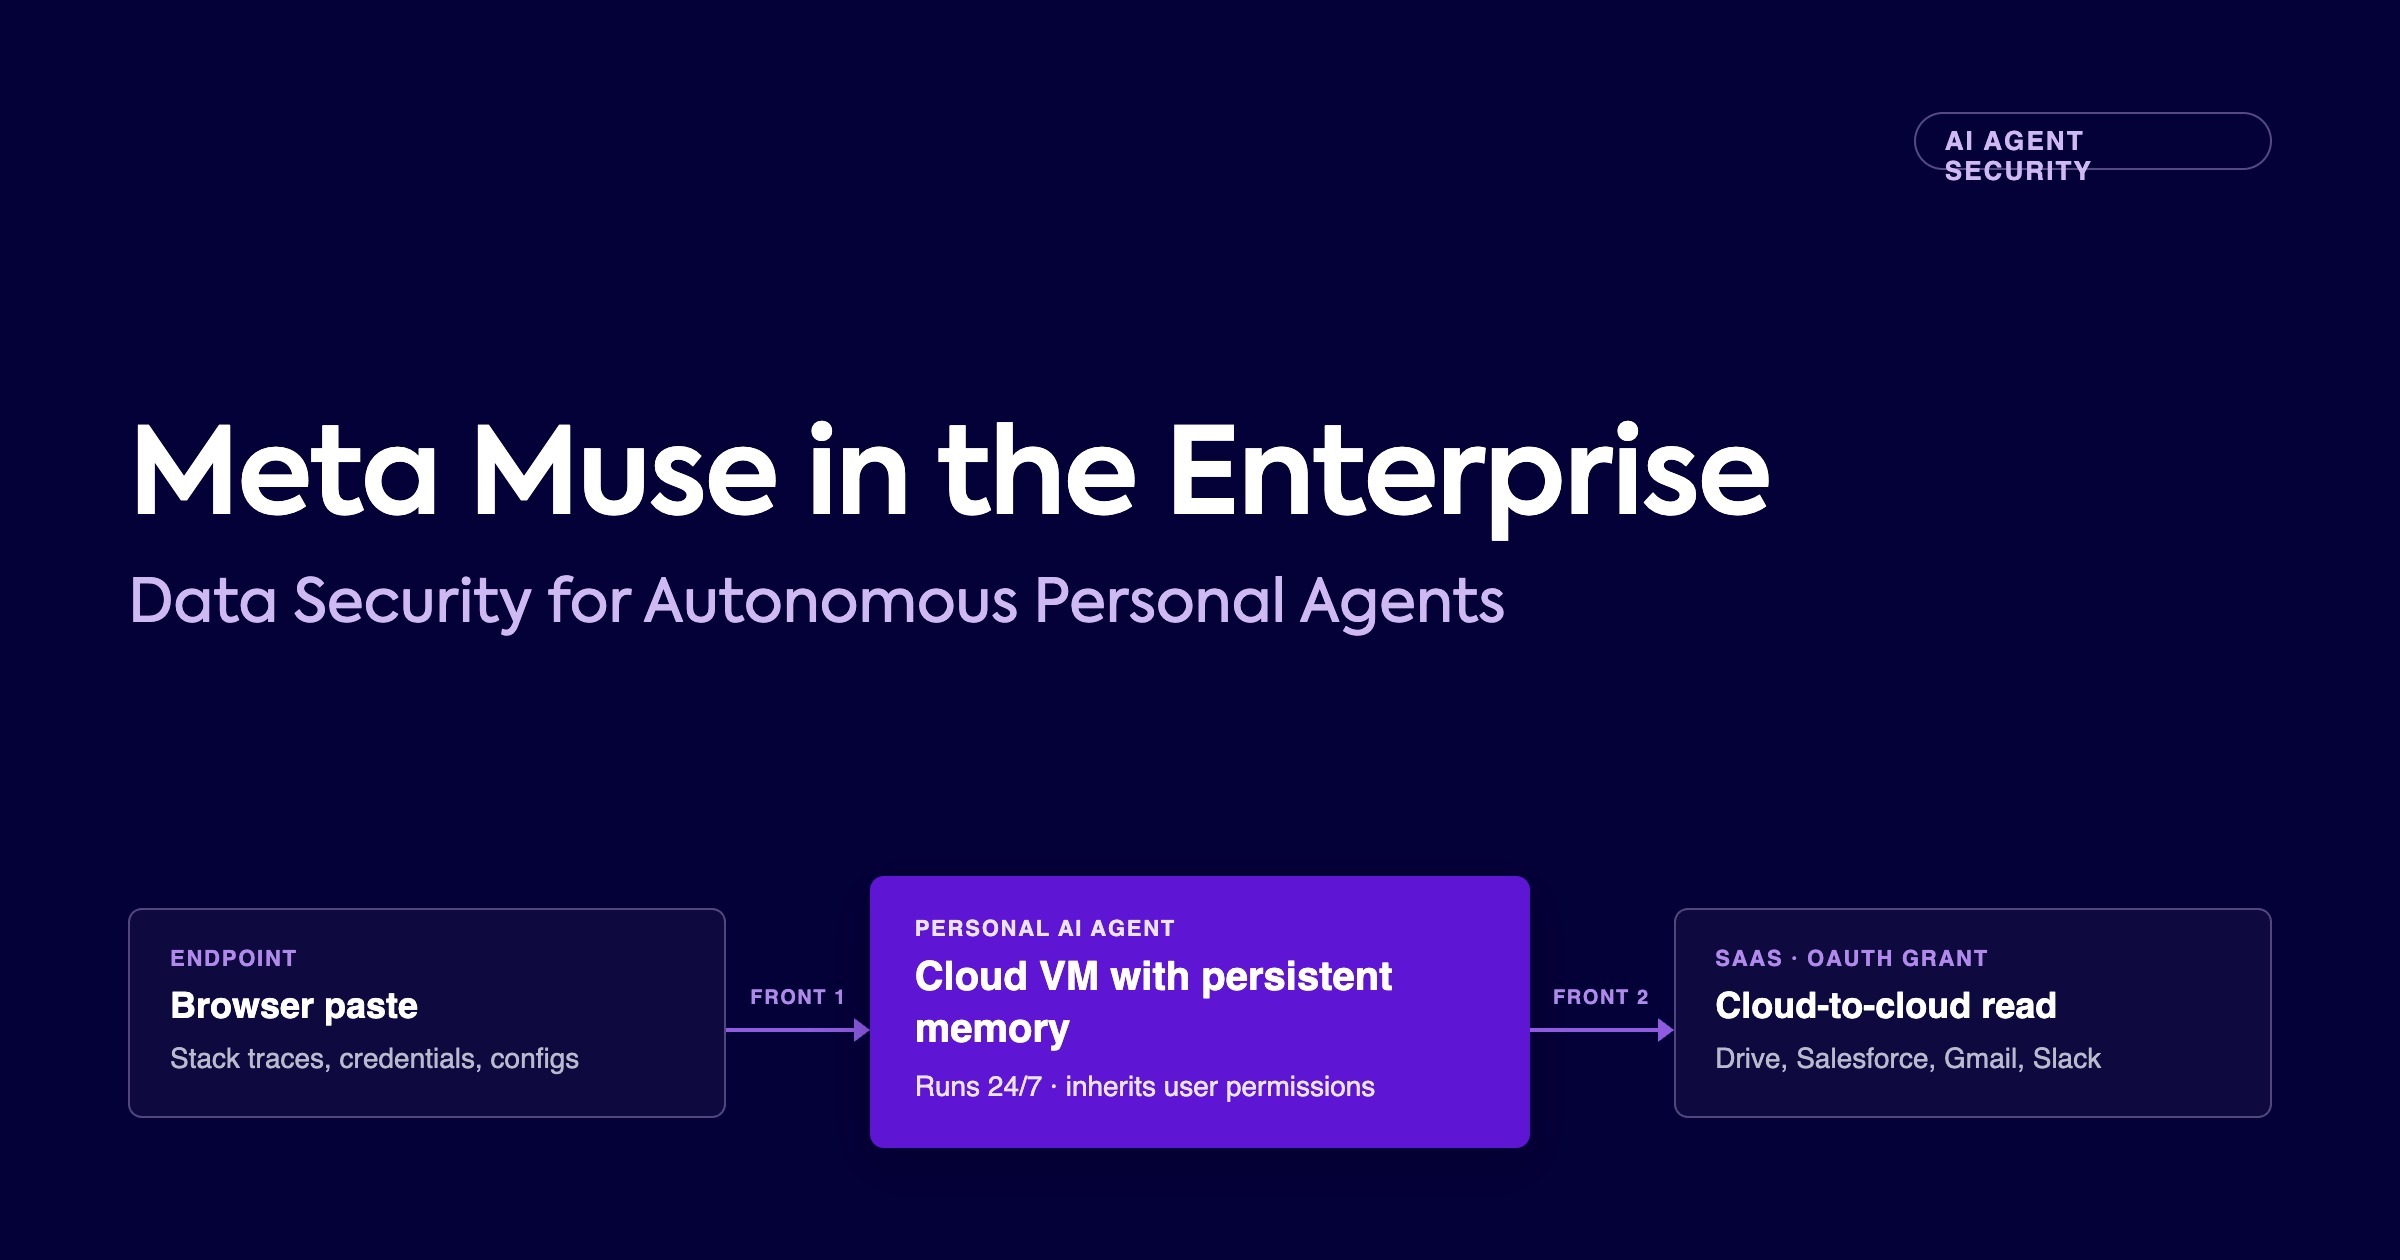
The deployment of personal AI agents like Meta's Muse represents a structural shift in enterprise data loss prevention. Unlike conversational web chatbots where data movement is limited to manual user prompts, autonomous personal agents operate in cloud virtual machines, run continuous background tasks, and connect directly to enterprise SaaS platforms through OAuth integrations.
This creates a dual-vector data loss problem that conventional security architectures evaluate in silos: direct endpoint egress through browsers, and automated cloud-to-cloud extraction via third-party application grants.
Telemetry across enterprise endpoints highlights how quickly these tools establish a footprint. When a consumer agent launches, initial usage typically begins within hours. More than 75% of early data movement occurs via clipboard pastes rather than file uploads, initiated by individual employees looking to accelerate daily workflows. In over half of observed environments, initial activity originates from a single user on a single device. Because new agent domains do not appear on web categorization feeds or legacy DLP destination lists, more than 95% of early interactions bypass destination-based controls entirely.
How personal agents move corporate data: Five operational workflows
Personal AI agents expose corporate data through high-utility delegation rather than malicious intent. When employees connect an autonomous agent to business tools, data moves across five common corporate workflows:
1. Engineering and DevOps: Production incident triage via browser paste
An on-call engineer debugging an outage pastes an application stack trace, database query, or environment configuration into the agent interface to identify the failure root cause.
- Data movement: Direct endpoint clipboard paste into the agent's web interface.
- Data at risk: Hardcoded database credentials, AWS IAM secret keys, internal service hostnames, API tokens, and proprietary backend logic.
- Exfiltration mechanics: Over 75% of early data movement into AI tools occurs through text pastes rather than file uploads. Web filters and secure web gateways miss these transactions because emerging agent domains lack established reputation ratings. Traditional DLP tools configured only to inspect file attachments overlook the clipboard stream entirely. The sensitive configuration enters external cloud vector storage and persistent cross-session memory outside corporate secret-rotation workflows.
2. Executive Office: Strategic planning and financial synthesis via file stores
A chief of staff or finance lead links the agent to corporate Google Drive or Box storage to prepare for a board meeting: "Review our last three board decks and draft an executive briefing summarizing Q3 revenue forecasts."
- Data movement: Cloud-to-cloud OAuth read executing directly between the agent cloud VM and Google Workspace APIs.
- Data at risk: Unreleased quarterly revenue figures, margin targets, M&A pipeline data, and executive strategy memos.
- Exfiltration mechanics: The transaction executes server-to-server, completely bypassing managed endpoint sensors and network proxies. Because the agent inherits the employee's full data access permissions, it can read any file the user can open, including legacy shared drives accessible to the entire company. The extracted strategic context is parsed and retained in the agent's persistent cloud storage.
3. Revenue Operations: Pipeline extraction via CRM connectors
An enterprise account executive connects the agent to Salesforce or HubSpot via Zapier or custom API connectors to automate deal updates: "Summarize all closed-lost enterprise opportunities over the last two quarters and identify recurring pricing objections."
- Data movement: Programmatic bulk queries via third-party API integration.
- Data at risk: Customer PII, contractual deal terms, ARR metrics, discounting schedules, and customer negotiation logs.
- Exfiltration mechanics: To evaluate qualitative questions across hundreds of accounts, the agent executes bulk API queries. In standard CRM audit logs, this access appears under the account executive's normal user credentials, masking the third-party application performing the extraction. Moving customer records and non-public financial terms into an unvetted consumer AI environment bypasses Data Processing Agreements (DPAs) and creates unmonitored regulatory exposure.
4. Human Resources and Legal: Continuous mailbox triage
An HR business partner connects corporate Microsoft Outlook or Gmail to automate inbox management: "Monitor incoming messages, summarize employee relations issues, and draft initial responses."
- Data movement: Continuous background mailbox synchronization via Microsoft Graph or Gmail APIs.
- Data at risk: Employee compensation spreadsheets, performance improvement plans, harassment complaints, health leave requests, and pending litigation correspondence.
- Exfiltration mechanics: Unlike on-demand chatbot prompts, mailbox connectors poll and index communications around the clock without manual intervention. If the employee departs the company and IT remotely wipes their laptop, the OAuth token stored in the agent cloud infrastructure remains active until administrators explicitly audit and revoke third-party application permissions in the identity provider.
5. Cross-Functional Collaboration: Inbound routing and indirect prompt injection
A procurement lead forwards vendor negotiation threads to the agent's inbound address or connects the agent to an external vendor coordination Slack channel.
- Data movement: Inbound email routing and bidirectional messaging webhooks.
- Data at risk: Vendor banking coordinates, invoice approvals, Master Services Agreements (MSAs), and internal communication history.
- Exfiltration mechanics: Forwarding unredacted email threads routes confidential contracts and message history to external mail servers outside enterprise archiving controls. Furthermore, when an agent processes untrusted external content (such as an invoice or email from an outside vendor) containing hidden instructional text, the agent becomes susceptible to indirect prompt injection. If manipulated, an agent with delegated write permissions can be directed to dispatch sensitive data to external endpoints or third-party webhooks.
Key attributes of an AI data loss prevention architecture
Addressing both browser-based egress and cloud-to-cloud extraction requires five core technical capabilities:
- Content-aware endpoint inspection over destination lists. Web categorization feeds and URL blocklists cannot keep pace with new AI releases. Data security must inspect the actual content moving across clipboard and browser streams on the device, evaluating data sensitivity in real time rather than relying on site reputation.
- Contextual session differentiation. Controls must distinguish an employee's personal account from an authorized corporate workspace on the same domain. This allows productive use of sanctioned business tenants while preventing data transfers into personal profiles.
- Source-side application attribution in SaaS. In cloud platforms like Google Workspace and Salesforce, data protection platforms must attribute file access, report exports, and API queries to the specific third-party application ID or service account involved, rather than logging the event solely under the human user's identity.
- Continuous forensic telemetry. Security teams need visibility into all data movements, capturing forensic event trails even when no explicit policy violation triggers. This baseline telemetry reveals unsanctioned agent adoption weeks before static policies can be authored.
- Unified cross-surface detection. Endpoint prevention and SaaS data governance must share a single detection brain. The same classification engine that monitors sensitive data in cloud repositories must enforce policy when that data moves across the endpoint or is accessed by an external API connector.
Nightfall provides this unified architecture. On the endpoint, Nightfall monitors browser uploads and clipboard pastes, differentiating personal from corporate accounts and enforcing policy on sensitive content. In cloud environments, Nightfall scans SaaS repositories and attributes data access in Google Drive and Salesforce to the originating application. By unifying content detection across devices and enterprise clouds, organizations can safely govern AI adoption without relying on fragile destination lists.


